Advertisement
Regulation & Policy
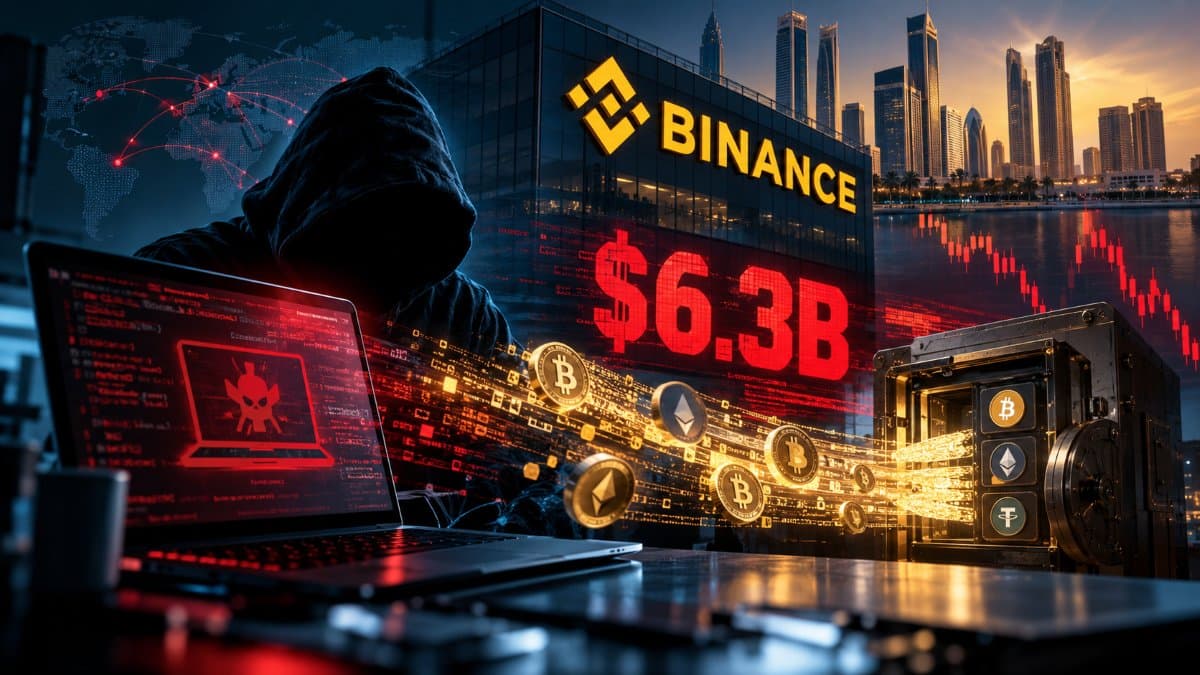
The Binance hack raises questions about how a compromised employee device allegedly enabled unauthorized withdrawals, echoing the Bybit attack and challenging institutional security controls as financial operations become increasingly automated.
Share
WA
CEO & Editor-in-Chief


A compromised DevOps engineer's laptop allegedly enabled unauthorized withdrawal transactions totaling an estimated $6.3 billion at Binance on October 29, triggering $1.55 billion in leveraged liquidations and prompting industry-wide asset freezes. The incident echoes the February 2025 Bybit hack and exposes structural weaknesses in financial authorization controls at major crypto exchanges.
The Binance hack, involving an estimated $6.3 billion in affected crypto assets, has exposed a fundamental question about the security architecture of the world's largest cryptocurrency exchange: how could a compromised employee laptop allegedly become an entry point for unauthorized transactions worth billions of dollars?
The incident, which unfolded on October 29, intensified a cryptocurrency market sell-off accompanied by approximately $1.55 billion in leveraged liquidations. It also triggered an industry-wide effort to freeze affected assets, with Binance reporting that around $3 billion had been frozen on-chain.
Yet the most consequential question may lie beyond the financial damage. Binance's preliminary explanation suggests that the attacker gained access through a compromised DevOps engineer's laptop.
The incident also bears similarities to the February 2025 Bybit hack, in which attackers exploited trusted wallet infrastructure to deceive authorized signers into approving a malicious transaction.
Together, the two incidents raise an institutional question: are financial authorization controls genuinely independent when the systems supporting them can be compromised?
In its official security incident update, published on October 30, Binance said its initial investigation suggested that a compromised DevOps engineer's laptop allowed an attacker to access an internal service container and submit unauthorized withdrawal transactions.
The exchange stated:
We have found no evidence of any wallet private key leak.
Binance estimated the total impact at approximately $6.3 billion and reported that around $3 billion in affected assets had been frozen on-chain through cooperation with blockchain partners.
It committed to covering all losses using its Secure Asset Fund for Users (SAFU) and corporate funds, while assuring customers:
User funds are safe.
As immediate precautions, Binance temporarily suspended deposits and withdrawals, revoked the affected address authorization, and engaged law enforcement and blockchain intelligence partners to trace the assets and identify those responsible.
The exchange also committed to publishing a detailed technical post-mortem once its investigation is complete and the facts have been verified, alongside an updated Proof of Reserves following remediation.
In subsequent communications, co-CEO Yi He indicated that deposits were operating normally while the exchange worked on its withdrawal infrastructure and related address controls. Withdrawals were expected to resume gradually within 48 hours, although this remained a target rather than confirmation of restored operations.
The complete technical sequence between the initial compromise and the unauthorized transactions remains unresolved.
The laptop explanation is striking, but it should not be confused with evidence that a single engineer possessed unrestricted authority over customer assets.
Binance has made no such claim.
A compromised workstation can expose credentials, privileged services or trusted applications. Attackers may then exploit additional vulnerabilities or manipulate systems operating beyond the employee's normal permissions.
The critical issue is therefore how the attacker moved from an initial compromise to the execution of unauthorized withdrawal transactions.
That question becomes particularly relevant given Binance's assertion that no private-key leakage has been identified.
An on-chain investigation by Bitquery identified transactions bearing valid signatures from affected Binance wallets, alongside unusual authorization activity involving Ethereum's EIP-7702 mechanism.
Blockchain security firm Blockaid has suggested that legitimate transaction-signing infrastructure may have been manipulated rather than private keys directly stolen. This remains a preliminary technical interpretation, not a confirmed explanation from Binance.
Protecting private keys is essential. But ensuring that the systems authorized to use those keys cannot be manipulated into executing fraudulent transactions is equally important.
Traditional financial controls seek to separate operational access, transaction initiation and independent authorization.
The underlying principle is straightforward: gaining access to a system should not automatically mean gaining authority to move assets.
The Binance incident bears notable similarities to the February 2025 Bybit hack, when attackers stole approximately $1.5 billion in digital assets by compromising infrastructure used to authorize wallet transactions.
According to Bybit's forensic announcement, issued on February 26, attackers compromised the credentials of a developer at Safe Wallet, an external multisignature wallet provider.
The compromised credentials enabled unauthorized access to Safe's infrastructure, where the attackers manipulated the transaction-approval process.
Authorized Bybit signers were subsequently deceived into approving a malicious transaction.
This distinction is significant.
Bybit had multiple authorized signatories. The attackers did not need to eliminate that arrangement or obtain direct control over every private key. Instead, they manipulated the environment through which legitimate approvals were obtained.
The FBI subsequently attributed the theft to North Korean cyber actors operating under the TraderTraitor designation.
More than a year later, Binance's preliminary explanation describes another compromised technical environment, although this time within the exchange's own operational infrastructure.
Blockaid CEO Ido Ben-Natan described the two attacks as: very, very similar.
His assessment centers on the possibility that Binance's signing infrastructure was manipulated into authorizing unauthorized transactions, rather than attackers directly extracting private keys.
However, the technical similarities remain preliminary. The Bybit attack involved an external wallet provider and deceived human signers, while Binance has yet to explain precisely how its withdrawal authorization systems were compromised.
The comparison nevertheless reveals a broader vulnerability.
Multiple approvals do not necessarily provide independent protection if those approvals depend on the same compromised technical environment.
The lesson from Bybit is not that segregation of duties is ineffective. It is that segregation must extend beyond the individuals approving transactions to the technological infrastructure on which their decisions depend.
For Binance, the investigation will need to establish whether automated authorization processes faced a comparable weakness.
The incident arrives less than a year after Binance transitioned its global platform to a regulatory structure under Abu Dhabi Global Market (ADGM).
Since January 5, 2026, Binance.com has operated through three entities supervised by ADGM's Financial Services Regulatory Authority (FSRA): Nest Exchange Limited, Nest Clearing and Custody Limited, and Nest Trading Limited.
The arrangement separates exchange operations, clearing and custody, and broker-dealer activities through distinct regulatory permissions.
In its ADGM launch announcement, Binance described the structure as reflecting established financial-market infrastructure, with clearer responsibilities and strengthened risk controls.
That institutional positioning makes the incident particularly relevant.
ADGM's guidance on virtual asset activities already addresses the concentration of financial authority.
Paragraph 153 prohibits authorized virtual asset custodians from maintaining arrangements in which a single party or signatory can completely authorize the movement or withdrawal of client assets.
The guidance also addresses collusion risks, records of authorized personnel and procedures for stopping transactions when assets may have been compromised.
These provisions demonstrate that segregation of duties is already embedded in ADGM's regulatory framework.
The question is how such safeguards operate within complex technology environments, where transaction approval may involve automated services, privileged accounts and software-based controls.
The Binance incident does not establish that the exchange breached ADGM requirements. Nor does legal separation between regulated entities necessarily reveal how technical authorization systems are configured.
Nevertheless, the comparison with Bybit raises a legitimate institutional question: can authorization controls be considered genuinely independent if a compromised software environment can influence several stages of the approval process?
The market reaction also reflected Binance's central role in global cryptocurrency trading.
According to CoinMarketCap's September 2026 exchange report, Binance processed approximately $2.13 trillion in combined spot and derivatives trading volume, accounting for 44.03% of activity across the 11 exchanges included in the study.
An operational disruption at a platform of this scale has consequences extending beyond its direct customers.
As reports of the incident spread, Bitcoin fell below $77,000, while Ethereum, BNB and other major cryptocurrencies experienced significant declines.
Data reported by The Block, citing CoinGlass, showed approximately $1.55 billion in cryptocurrency derivatives liquidations over 24 hours, including $1.34 billion in leveraged long positions.
The concentration of long liquidations suggests that forced deleveraging substantially amplified the sell-off.
When prices decline in highly leveraged markets, automatic position closures create additional selling pressure, potentially triggering further liquidations.
This cascade can produce market movements disproportionate to the initial shock.
However, the figures do not establish that the Binance incident caused every liquidation. Existing market positioning and broader conditions also contributed to market vulnerability.
The reaction illustrates how Binance's market concentration can transmit operational disruptions across the cryptocurrency ecosystem.
It also highlights a distinction between financial strength and market stability.
Binance's reported resources and its commitment to compensate customers may help contain concerns about financial losses. But the exchange's financial resilience does not automatically prevent liquidity disruptions, forced liquidations or volatility across interconnected markets.
Its size is therefore both a potential source of resilience and a reason why operational incidents can have market-wide consequences.
Binance's leadership has emphasized customer protection and the exchange's ability to absorb losses.
Co-CEO Richard Teng acknowledged the investigation and reassured users that their assets remained safe.
Fellow co-CEO Yi He confirmed that Binance would cover hacking losses, while subsequent communications addressed the temporary suspension of withdrawals and efforts to strengthen the affected infrastructure.
Binance founder Changpeng Zhao, widely known as CZ, acknowledged the apparent breach on X, writing: It does look like a hack on Binance.
Zhao thanked Tether and Circle for their rapid intervention in freezing affected assets. He also clarified that he no longer manages Binance.com, although he remains a shareholder, and expressed confidence that customer funds would be fully covered.
The intervention of stablecoin issuers and other ecosystem participants has been significant.
Tether reported freezing more than $1.5 billion in USDT associated with the incident, while Circle froze more than $800 million in USDC. Other industry participants also assisted in restricting the movement of affected assets.
Nevertheless, frozen assets are not necessarily recovered assets. The final financial impact will depend on the recovery process and Binance's remediation efforts.
The leadership's financial assurances address immediate customer concerns. They do not eliminate the need to understand how unauthorized transactions passed through the exchange's operational infrastructure.
The Binance and Bybit incidents also raise a forward-looking question about the evolution of operational controls as financial institutions increasingly explore autonomous AI agents.
There is no evidence that AI agents were involved in either breach.
Nevertheless, the attacks demonstrate how compromising trusted infrastructure can undermine authorization processes, even when multiple parties or technical safeguards are involved.
As AI agents begin interacting with APIs, preparing transactions, managing liquidity and executing operational workflows, the same vulnerability could become more consequential.
An exchange could deploy one AI agent to monitor liquidity, another to prepare transfers and a third to approve transactions.
Yet such an arrangement would not necessarily provide independent authorization if the agents share credentials, permissions, infrastructure or common decision-making dependencies.
Multiple autonomous agents performing different tasks do not automatically represent independent financial authorities.
The UAE has already established regulatory foundations relevant to this challenge.
Dubai's Virtual Assets Regulatory Authority (VARA) has published technical standards addressing privileged access, developer workstations, segregation of duties and transaction verification.
Separately, the UAE Central Bank's 2026 guidance on responsible AI and machine learning emphasizes meaningful human oversight, accountability and risk-based limits on autonomous decision-making.
These frameworks operate within distinct regulatory jurisdictions and should not be interpreted as automatically applying to Binance's ADGM-regulated entities.
However, they illustrate how established financial controls are beginning to intersect with the governance of increasingly autonomous systems.
The emerging question is whether existing requirements need more explicit provisions for AI agents capable of initiating transactions or influencing financial authorization.
Such provisions could address genuinely independent authorization boundaries, transaction limits, auditability, human oversight and emergency suspension mechanisms.
The objective would not be to replace segregation-of-duties principles, but to ensure they remain effective when financial responsibilities are delegated to software.
The Binance incident should not be interpreted as evidence that the exchange is financially insolvent, that one employee-controlled billions of dollars or that its regulators failed to establish adequate standards.
None of those conclusions has been demonstrated.
What the breach does raise is a question about the relationship between regulatory structures, institutional commitments and the actual operation of security infrastructure.
The Bybit precedent is particularly relevant because it demonstrated how legitimate transaction approvals could be manipulated through compromised technology.
Binance has evolved into a globally significant financial intermediary, with substantial trading volumes, sophisticated custody operations and a regulatory structure designed to reflect established financial-market practices.
Its ability to protect customers financially after an incident is important. So is its ability to demonstrate how unauthorized transactions can be prevented, detected and contained.
The promised technical post-mortem should provide further insight into the attack sequence, affected systems and the safeguards involved.
As exchanges become more deeply integrated into global financial markets, and as AI agents assume financial responsibilities previously performed by people, the implications extend beyond Binance.
If a compromised technical environment can undermine financial authorization systems, how can institutions ensure that no individual, internal service or autonomous agent gains unchecked authority over customer assets?

Disclaimer of Warranty
The information provided in this article is for general informational purposes only. We make no warranties about the completeness, reliability, and accuracy of this information. Read full disclaimer

Editor's Picks
In the Same Space
Crypto Ads in the UAE Face New Google Rules Starting October 21

News Desk

Oct 20, 2026

4 min
VARA Expands PRYPCO License as Real Estate Tokenization Evolves
Salma Naueihed
Oct 29, 2026
5 min
ADGM Publishes Dedicated Crypto Mining Guidance
News Desk
Oct 28, 2026
2 min
Robinhood Plans Dubai Launch in 2027 After DFSA Authorization
Walid Abou Zaki
Oct 22, 2026
4 min